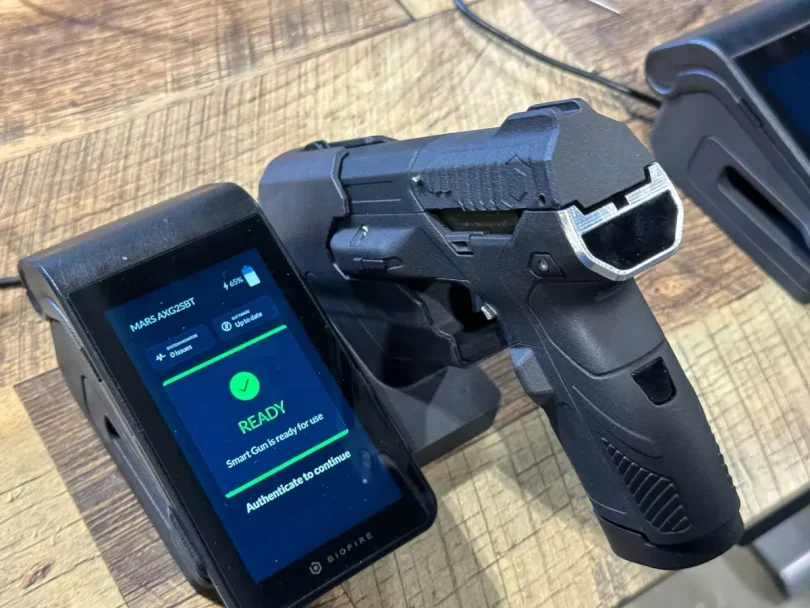
The safe in the closet is a witness now. A modern biometric gun safe doesn’t only lock. It remembers. Every finger placed on the scanner, every door open, every failed attempt, every low-battery ping to a phone across the house. That memory used to sit on a chip nobody looked at. In federal firearms cases, it’s starting to sit on a prosecutor’s exhibit list.
The shift is real, and it’s picking up speed. Prohibited-person cases, straw purchase investigations, and possession charges tied to drug offenses all turn on the same hard question: who had access, and when. A safe that logs its own openings answers that question in a way a shoebox on a shelf never could. Sometimes for the defense. Sometimes very much not.
Contents
The Log Is Already Being Written
Most buyers pick a biometric safe for speed and for keeping curious kids out. The audit trail is a footnote in the manual. But it’s running from the moment the safe is powered on, and it captures more than owners realize: enrolled fingerprint IDs, timestamps for each open, tamper alerts, and, on connected models, a mirror of all of it in a phone app and often on the manufacturer’s cloud.
A National Institute of Justice review of gun safety technologies walks through how biometric and RFID access systems authenticate users and record those events. That record is the same data an investigator will later ask for. When charges involve who could reach a firearm, the log stops being a convenience and becomes evidence.
How it gets used often collides with the Second Amendment and possession defense strategy built around that exact question. Investigators know what to ask for. So do co-defendants.
Why “I’ll Just Say I Never Opened It” Falls Apart
The obvious defense move in a possession case is to distance the client from the gun. Someone else lived there. Someone else had access.
The client hadn’t touched the safe in weeks. On paper, it’s a clean story. The log rarely lets that story stand. If the client’s fingerprint is enrolled as User 01, and User 01 opened the safe late the night in question, the timeline the defense hoped to build collapses before it starts. Worse, the phone app tied to that safe usually shows which paired device received the tamper alert, and whose thumb dismissed it. Denying access to a device that timestamped its own use tends to make a jury doubt everything else the defendant says.
There’s a second problem with the intuitive fix. Even if the physical safe is emptied or reset, the cloud copy often persists. The device forgets. The account remembers.
The Records Aren’t Automatically Admissible, Either
Prosecutors still have to get the log in. That means authentication under the rules of evidence, a clean chain of custody running through safe, server, and exhibit, and a witness who can explain what the entries actually mean.
A legal analysis of IoT devices as digital witnesses lays out the friction points: Rule 901 authentication, Fourth Amendment questions about cloud-stored data, and spoliation risk when a party lets logs cycle out.
Each of those is a live fight. A default fingerprint label of “User 01” doesn’t, by itself, name a human. Timestamps drift when clocks aren’t synced. A tamper alert can be triggered by a dropped safe as easily as a pry bar.
None of that makes the log worthless, but it does mean the defense has real ground to challenge on.
What Actually Works Once a Safe Is in the Case
- Preserve everything, immediately. Pull the app history, export the log, and note the firmware version before anyone “tidies up” the device. Data that cycles out on a 30- or 90-day window is gone when the subpoena finally lands.
- Get the enrollment map. Ask who enrolled each fingerprint and when. “User 01” is a label, not a person, and the government has to bridge that distance.
- Cross-check the timeline. Line safe opens against phone location data, doorbell cameras, and alarm-panel arm/disarm logs. Contradictions between devices are where reasonable doubt lives.
- Push on the warrant. Cloud-stored biometric logs sit in the same evolving Fourth Amendment territory as phone data. A warrant that sweeps in everything the account ever recorded, with no time or offense limit, is worth challenging on particularity grounds.
- Talk to counsel before you talk to anyone else. Statements about who “usually” opens the safe age badly once the log is on the table. The safer move is to say nothing about access patterns until a lawyer has seen the data the government has.
The safe was supposed to keep a firearm out of the wrong hands. It still does. It also keeps a receipt, and in a federal case, that receipt gets read out loud.